Abacus R&D Finds an 802.1X Bypass and a Credential Exposure in Cisco ISE
Abacus’ R&D team found two vulnerabilities in Cisco Identity Services Engine (ISE), a platform that enforces 802.1X access controls on corporate networks and is typically deployed as a physical or virtual appliance.
Despite 802.1X access controls being touted as the “gold standard” for enterprise authentication, the first vulnerability allowed an unauthenticated attacker to bypass 802.1X EAP-TLS and reach secure enterprise networks. The second vulnerability allowed an authenticated management user to read passwords for network users outside their own security group.
As of September 16, 2026, Cisco has released patches for both critical vulnerabilities.
Hijacking 802.1X Onboarding
The first vulnerability allowed an unauthenticated attacker to hijack a user’s 802.1X onboarding workflow in ISE and gain access to 802.1X-protected networks. Cisco recommended performing 802.1X onboarding over open, unencrypted wireless networks and designed the workflow to rely on a single factor: the session ID. Session IDs were generated deterministically. The R&D team determined that an attacker only needed a victim who attempted onboarding within wireless range to begin their process. R&D captured the session ID by listening to unencrypted wireless traffic, as shown below. In theory, an attacker could also calculate the session ID directly, or obtain it by spoofing the victim’s MAC address (the hardware identifier a device broadcasts), connecting to the network, and requesting the redirect to the onboarding wizard.
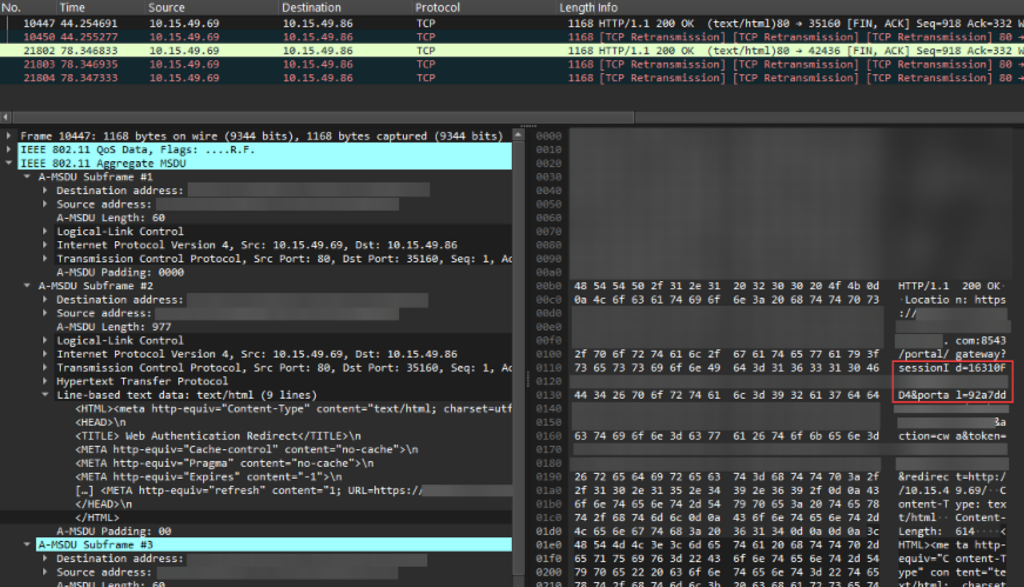
The session ID was captured by observing unencrypted wireless network traffic.
With the victim’s session ID, an attacker could begin the onboarding process by submitting a well-formed request to the provisioning endpoint, the part of ISE that handles device setup. This was the same process completed by Cisco’s Network Setup Assistant and was no different from the intended enrollment workflow.
During onboarding, an attacker could obtain the XML configuration and a challenge password, a one-time code that authorizes the final step. The password was then used to finalize onboarding and submit a Certificate Signing Request (CSR) for a keypair the attacker generated. Once ISE received the attacker’s CSR, it issued a client certificate for authenticating to 802.1X-protected networks.
Because this certificate was issued through the victim’s hijacked session, the attacker could then authenticate to 802.1X-protected networks, posing as the victim.
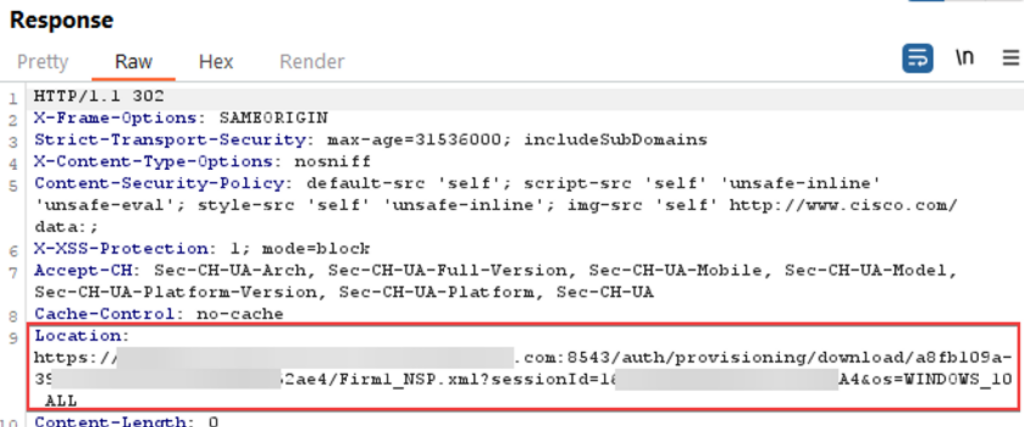
The provisioning endpoint accepted the stolen session ID and redirected the attacker to the configuration XML.
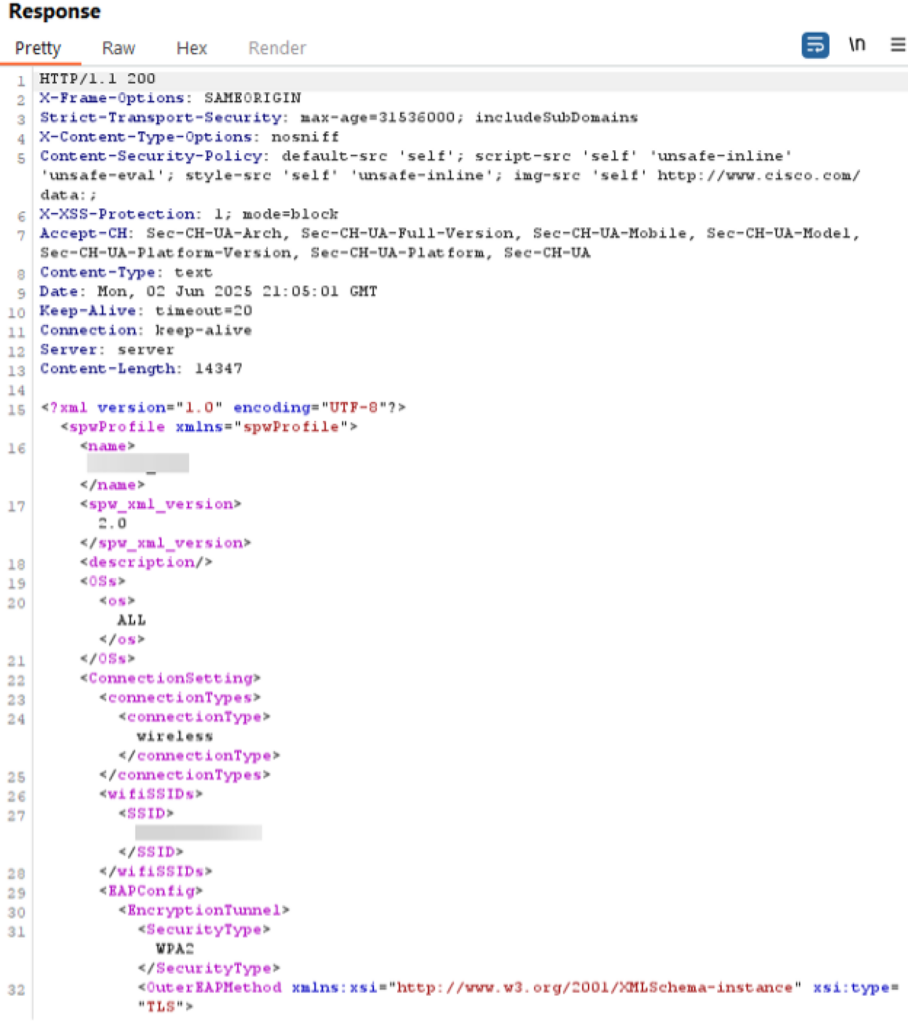
The XML configuration returned to the attacker specified wireless connection settings and EAP-TLS for the protected network.
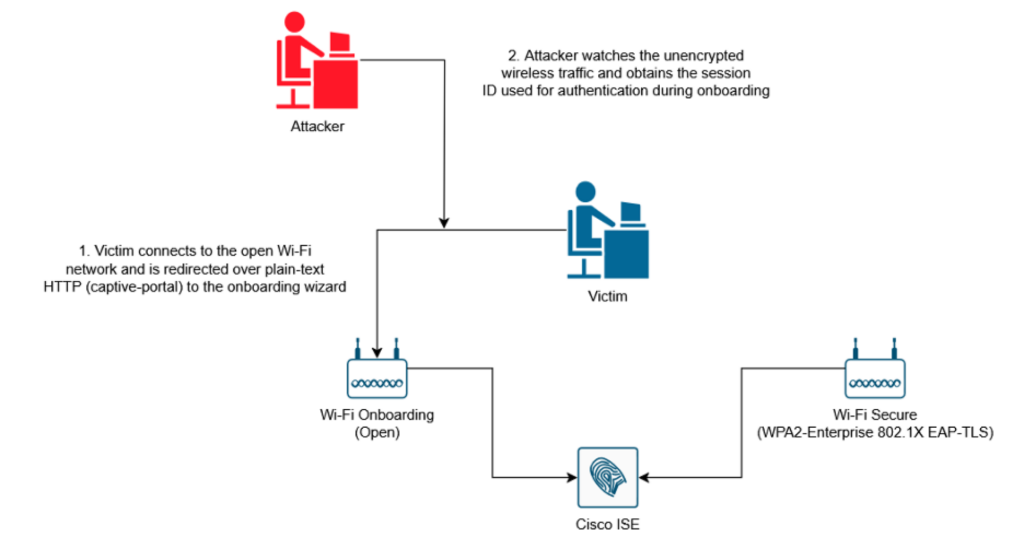
Attack path, steps 1 and 2: the victim onboards over the open network while the attacker reads the session ID from the traffic.

Attack path, steps 3 and 4: the attacker uses the session ID to reach the provisioning endpoint and download the onboarding XML.

Attack path, steps 5 and 6: the attacker submits a CSR and ISE returns a signed certificate.
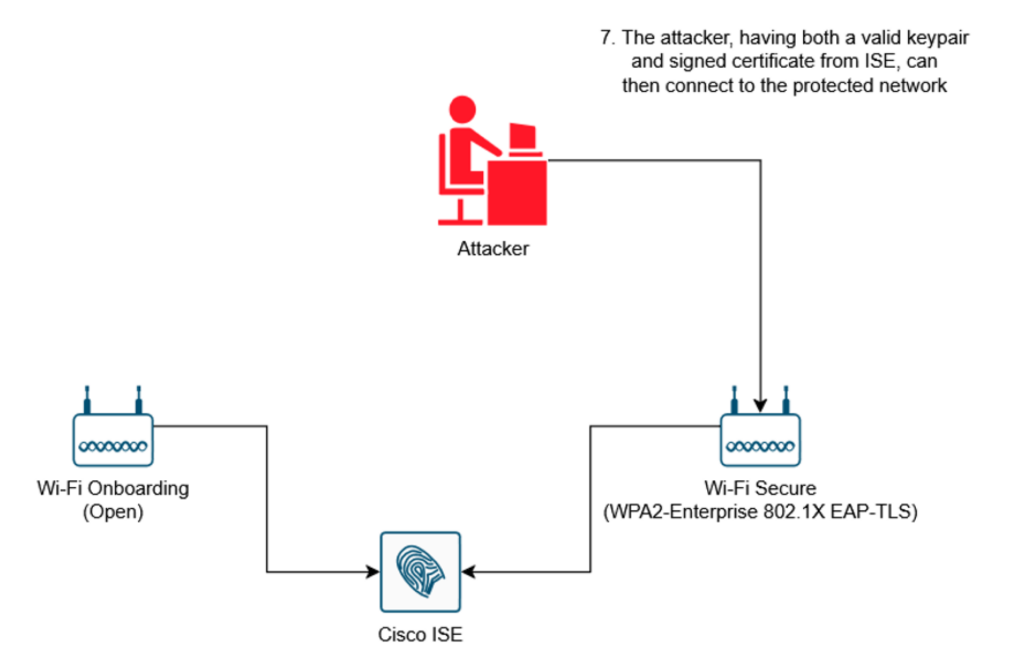
Attack path, step 7: the attacker connects to the protected network with the issued certificate.
Exporting Credentials Across Security Groups
The second vulnerability required an attacker to be authenticated to Cisco ISE and have management rights over network users in their assigned security group. With those rights, an attacker could export user credentials outside the attacker’s assigned security group. The only information necessary for this attack to succeed is the target’s username.
The attack uses ISE’s own user export function. An export request includes a “_QPC_” cookie that identifies which users to export. Because this value is only encoded, an attacker could decode the cookie, replace the target user with the name of a user in another security group, re-encode it, and resubmit the request. The endpoint then returned the victim’s user information without verifying that the requesting manager was authorized to export that user. Any management user could disclose credentials for users well outside their intended scope.
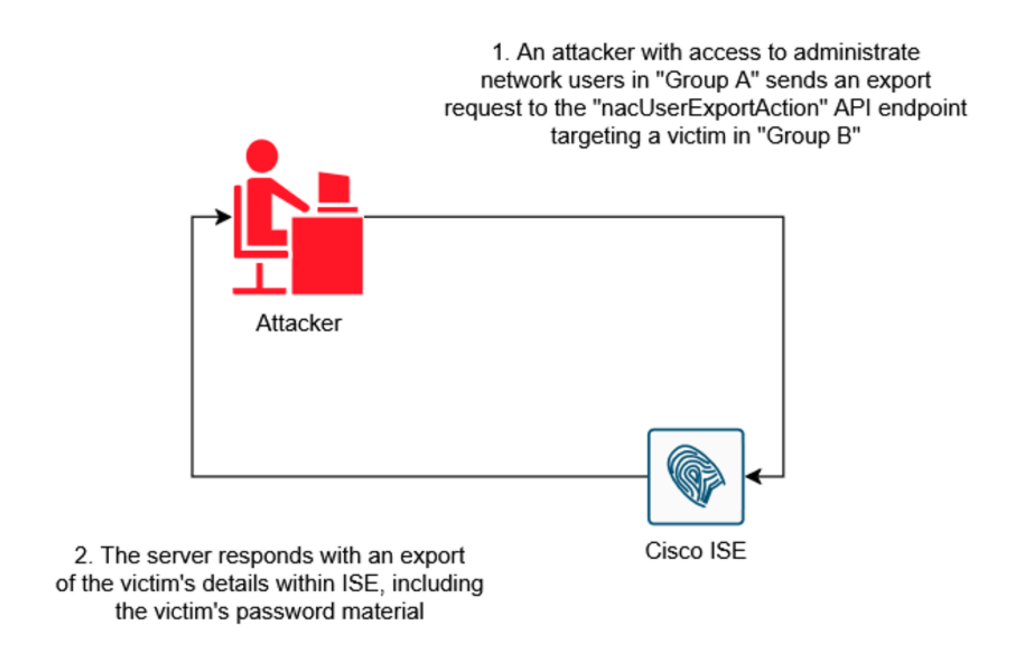
Attack path: a manager in one security group exports a user from another, and ISE returns the victim’s password material.
Disclosure and Remediation
Abacus reported both vulnerabilities responsibly through Cisco’s Product Security Incident Response Team (PSIRT), and Cisco assigned CVE-2026-20071 and CVE-2026-20072. Organizations running affected versions of Cisco ISE are strongly encouraged to apply the relevant updates. Cisco remediated both findings as of September 16, 2026. Cisco’s security advisory:
Abacus remains committed to responsible disclosure practices that give vendors the time needed to protect their customers before technical details are made public. Abacus thanks Cisco for its partnership and remediation of these issues, as well as R&D’s Dennis Carlson and Andres Lara for their research.
Abacus’ R&D team tests the security tools that organizations depend on and reports what it finds to the vendors. The same work informs how Abacus protects its clients in regulated industries like financial services and healthcare, helping them remain resilient to threats as they emerge.
To talk with our team of experts about your security program or to evaluate your security posture with an assessment, contact Abacus.